150,000 memory intercepts per second—that is the cost of running Windows games on one of the world’s most security-conscious operating systems. On October 20, 2026, OpenBSD released its 61st official release, version 8.0. On the same day, developers submitted experimental patches to the ports mailing list to bring Wine to the platform.
Initial tests confirm that multiple 64-bit applications, including The Witcher 3: Wild Hunt (Next-Gen), run successfully. Long regarded as an unyielding fortress of network security, the venerable Unix derivative has opened a window to the modern proprietary software ecosystem through low-level emulation and pragmatic engineering.
 Figure: Still from the OpenBSD 8.0 release animation “Blowfish on a Bike,” where mascot Puffy rides forward, symbolizing steady progress toward modernization. Source: OpenBSD (openbsd.org/images/blowfishonbike.mp4)
Kernel Virtual Address Space Expands to 512GB for Modern GPUs
The most consequential architectural change in OpenBSD 8.0 lies in its virtual memory subsystem. Previously, the amd64 kernel virtual address space was restricted to a modest 4GB window. Faced with modern hardware demands, that limitation had become a severe bottleneck.
Modern discrete GPUs rely heavily on Base Address Register (BAR) resizing mechanisms, where VRAM mappings frequently require contiguous windows spanning tens of gigabytes. While the previous 4GB ceiling effectively blocked high-memory GPUs, expanding the address space to 512GB provides the necessary operating headroom for massive VRAM mapping.
With address constraints lifted, OpenBSD merged the DRM subsystem from Linux 6.18.53 into its kernel graphics stack. The driver overhaul covers inteldrm, radeondrm, and amdgpu, bringing official support for Intel Arc A-series discrete graphics for the first time.
Porting Linux kernel graphics drivers directly is a deliberate trade-off given community resource constraints. The team rewrote kernel synchronization primitives and bus adaptation layers to ensure external driver code adheres strictly to OpenBSD’s own memory management discipline.
Pragmatic trade-offs also guided hardware architecture maintenance: OpenBSD 8.0 officially retired the long-supported Loongson MIPS platform, while completing suspend and resume support on arm64.
Retiring legacy architectures reduces the burden of cross-compilation and maintenance, allowing engineering effort to focus on active 64-bit systems and keeping the core codebase lean and nimble.
Intercepting 150,000 Accesses per Second: Bridging gsbase via Emulation
Alongside the 8.0 release, technical communities were electrified by an experimental Wine port posted to the OpenBSD mailing lists. Spearheaded by developers Andrii and Fabien, the patchset demonstrated dozens of 64-bit Windows applications running smoothly, ranging from Notepad++ to demanding commercial titles like The Witcher 3: Next-Gen.
Running proprietary binaries was never OpenBSD’s primary mission. However, this breakthrough turned theoretical discussion into real-world viability. For the first time, the security-hardened Unix system showed it could support complex consumer software.
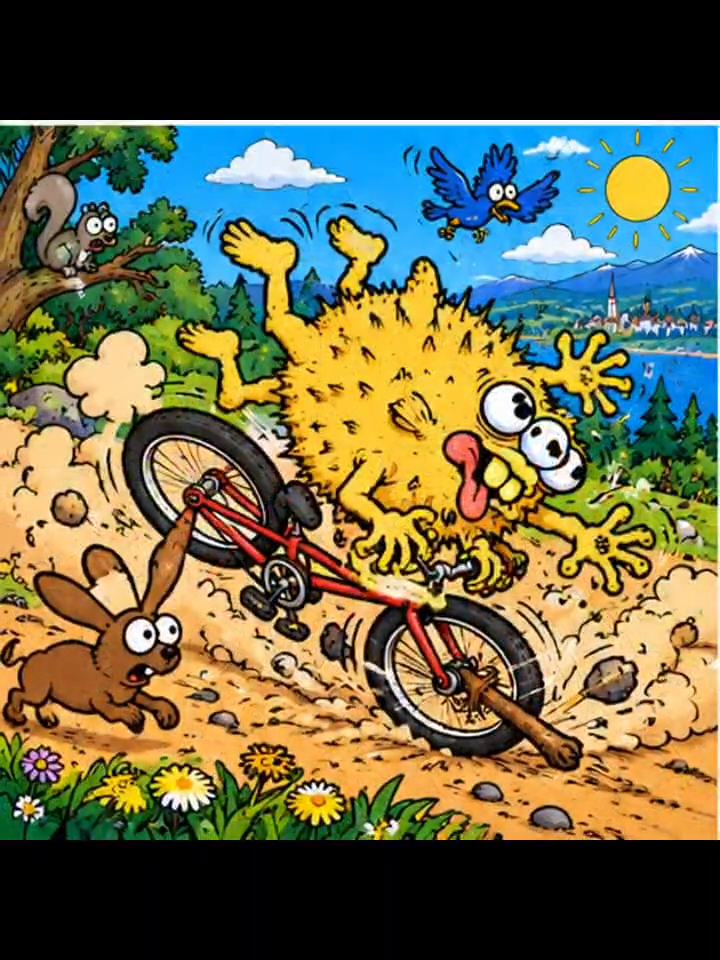 Figure: Scene detail from “Blowfish on a Bike,” highlighting the humor and uncompromising independence that define OpenBSD’s community culture. Source: OpenBSD (openbsd.org/images/blowfishonbike.mp4)
The thorniest engineering hurdle in porting Wine was segment register base management. Windows binaries rely extensively on %gs to locate the Thread Environment Block (TEB). By design, OpenBSD strictly prohibits unprivileged user-mode processes from directly manipulating gsbase.
Rather than relaxing kernel protections, the developers opted to emulate %gs-prefixed instructions in software. On hot execution paths, the system intercepts and redirects roughly 150,000 accesses per second. By substituting frequent memory intercepts for privileged register access, the kernel preserves the strict boundary isolating user space from raw hardware state.
Trading runtime performance for absolute architectural isolation reflects OpenBSD’s defensive core philosophy. Without compromising its security model, the team constructed a bridge to an alien execution environment, balancing cleanliness with broader utility.
The approach has notable boundaries: WoW64 is not yet implemented, meaning 32-bit Windows binaries cannot run, and developers disabled the built-in test suite while reminding early adopters that use is at their own risk.
The community greeted the project with mixed reactions. While enthusiasts celebrated the ability to run modern titles, purists questioned whether external binary blobs might expand the system’s attack surface—a classic tension between ecosystem compatibility and minimal attack surface.
Built-In Hypervisor Enhancements and Sandbox Guardrails
Even as external workloads knock on the door, OpenBSD has reinforced its internal isolation boundaries. Version 8.0 introduces significant upgrades to its native hypervisor daemon, VMM, expanding guest support up to 64 vCPUs per virtual machine.
The virtualization stack also gained an x2APIC controller and hardware checksum offloading. Hardware offloading shifts checksum computations out of the hypervisor execution loop, slashing CPU overhead during high-throughput networking and preparing VMM for heavier multi-core workloads.
OpenBSD continues to keep its hypervisor inside the base system rather than relying on third-party frameworks. A unified code repository ensures scheduling and virtualization logic undergo identical security audits, eliminating hidden vulnerabilities caused by upstream dependency drift.
Users reported seamless upgrades from 7.6 to 8.0 with zero configuration breakage—a testament to the stability of an integrated base system where core components evolve in lockstep without fragmented environments.
Crucially, the bedrock of OpenBSD security remains untouched: pledge(2) and unveil(2) continue to govern privilege and filesystem access. In mailing list discussions, sandboxing Wine using unveil quickly emerged as standard practice.
Enclosing untrusted foreign runtimes inside mandatory sandboxes establishes an impenetrable perimeter. Alien software may execute within restricted boundaries, but critical operating system assets remain entirely out of reach.
Satirizing AI Hype: A Pragmatic OS Moving Forward Line by Line
 Figure: The official 200×200 pixel artwork for OpenBSD 8.0, titled “Blowfish on a Bike,” featuring the iconic mascot Puffy. Source: OpenBSD (openbsd.org/images/blowfish.jpg, artwork by yvaneht nioj and clanker)
OpenBSD 8.0 honors the tradition of releasing a custom theme song and poster with every milestone. This release features the artwork Blowfish on a Bike alongside the theme song The Simps on AI. The lyrics tongue-in-cheek reminisce about simpler times without artificial intelligence—when people relied on good old-fashioned human stupidity, and enjoyed it.
Developer bentley later noted that the AI commentary was merely humorous packaging. The core message is steadfast accountability: engineers must take personal responsibility for every single line of code they ship—a refreshing sentiment in an era of automated code generation.
OpenBSD’s stance toward external ecosystems remains pragmatic. From integrating modern graphics drivers to expanding virtual memory to 512GB, the underlying call paths were meticulously rewritten line by line to accept modern hardware on the system’s own terms.
The hurdles to Unix desktop adoption stem from deep divergences in ABI and kernel specifications rather than simple application porting. By restructuring low-level virtual memory and register handling without compromising security contracts, OpenBSD continues to demonstrate how a focused, disciplined system can bridge modern realities on its own terms.
Reference Links:
- OpenBSD 8.0 Release Announcement
- OpenBSD Ports Mailing List Thread on Experimental Wine Port
- Hacker News Discussion on Linux DRM Driver Porting and Kernel Addressing
- Hacker News Community Feedback on OpenBSD 8.0