12,000 Out of 47,000: Red Lights Flash Across the Trading Desk
In mid-October, Goldman Sachs issued a firm-wide technical memo barring traders and investment bankers from deploying third-party AI coding tools. What had been an open trial for autonomous agents was abruptly reined in. Out of roughly 47,000 employees across the bank, only around 12,000 software engineers retained authorization to run tools like Claude Code and GitHub Copilot.
The clampdown stands in sharp contrast to management’s enthusiastic messaging just months earlier. In July, Goldman Sachs CIO Marco Argenti publicly praised the concept of “vibe coding,” encouraging front-office business staff to build rapid software prototypes with generative models before handing them over to dedicated engineering teams for production hardening.
Barely three months later, that open experimentation ground to a halt at the trading desks. Outside of core technology divisions, Goldman preserved access only for front-office quantitative strategists (“strats”) responsible for mission-critical pricing and algorithmic models. Tool access criteria effectively reverted to physical seating: what desk an employee occupies now dictates the caliber of automation tools they are permitted to launch.
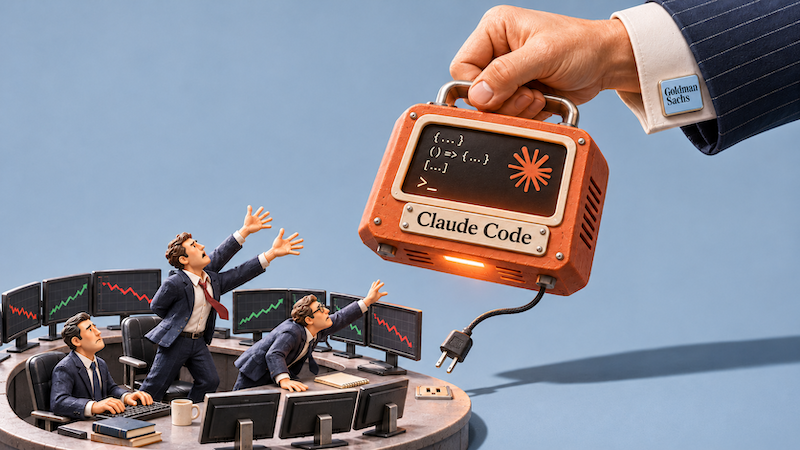 Figure: Report highlighting Goldman Sachs restricting AI coding tools across non-engineering divisions. Source: The State of AI
The move was foreshadowed by earlier compliance maneuvers. In April, Goldman suspended Claude access for Hong Kong-based dealmakers citing contractual compliance obligations, while retaining ChatGPT and Gemini on the approved whitelist. By June, JPMorgan Chase similarly struck Claude from its permitted software roster for Hong Kong teams.
Unreviewed Scripts and Autonomous Agents Shattering Chinese Walls
Autonomous coding agents differ fundamentally from traditional code-completion plugins. Conventional autocomplete functions merely as a glorified keystroke assistant inside an IDE, passively suggesting syntax snippets. Next-generation tools like Claude Code operate as autonomous command-line agents capable of inspecting local directory trees, editing configuration files, and executing shell commands on their own initiative.
Crucially, an autonomous agent inherits the full operating system permissions of its host user. On the workstations of traders and investment bankers, file systems routinely house unredacted, highly sensitive material: multi-million-dollar client order sheets, non-public M&A term sheets, and internal risk limits.
Engineering organizations enforce strict defensive boundaries. Code destined for production repositories must pass peer code reviews and run through sandboxed CI/CD test pipelines. Scripts whipped up by trading desks for quick statistical checks rarely face such scrutiny; instead, they frequently run ad-hoc scripts directly against live production data in local terminals.
Modern investment banking rests upon rigorous Chinese Walls. Securities regulations mandate absolute separation between investment banking divisions and secondary-market trading desks, prohibiting the flow of material non-public information (MNPI). The moment an autonomous agent indexes unredacted local documents across these boundaries, that foundational compliance firewall is compromised.
The Lethal Trifecta: Prompt Injections Meet System Execution
Security researchers model autonomous agent risk through the lens of the “lethal trifecta.” Whenever an agent combines access to private data, exposure to untrusted inputs, and external communication capabilities, the system becomes acutely vulnerable to hijacking.
A trader’s daily desktop environment checks every box of this high-risk model. Local terminals pull up confidential internal trade blotters and positions. Concurrently, those same terminals receive external counterparty chats, analyst notes, and internet market feeds—classic vectors for untrusted content.
If an incoming research attachment harbors a hidden prompt injection, scanning or parsing the document can prompt the agent to exfiltrate local portfolio positions via outbound web requests, instantly compromising the firm’s perimeter. While standard developer sandboxes can strictly lock down outbound network traffic, a front-office workstation cannot function without continuous, real-time external communications. Limiting which machines can run autonomous agents became the bank’s most pragmatic line of defense.
Beyond security and compliance vulnerabilities, compute costs played an immediate operational role in applying the brakes. Agents bill by token consumption, and multi-step autonomous reasoning loops can burn through computing budgets rapidly. Amazon previously shut down internal AI usage dashboards after employees flooded systems with low-value queries to game internal leaderboards. Accenture similarly placed a hard $29 monthly cap on Claude usage for standard personnel.
The Underwriting Paradox: Pitching Anthropic While Banning Its Agent
 Figure: Goldman Sachs global headquarters at 200 West Street in Manhattan. Source: Wikimedia Commons
The sudden rollback created an ironic juxtaposition on Wall Street. On October 26, AI maker Anthropic filed its S-1 registration statement, planning an initial public offering on Nasdaq under the ticker ANT. Goldman Sachs was selected as one of the lead underwriters for the landmark transaction.
Over the coming weeks, Goldman investment bankers are slated to tour global roadshows, pitching institutional investors on the commercial promise of Anthropic’s technology. Yet inside Goldman’s 200 West Street headquarters, the very bankers selling Anthropic stock are blocked by internal risk management from launching Anthropic’s autonomous coding agent on their work machines.
This institutional ambivalence runs throughout global finance. Barclays proclaimed in autumn that half of its software developers would adopt Claude Code before year-end. Barely three weeks later, Barclays announced plans to cut 5,000 jobs, with software engineers originally expected to achieve productivity breakthroughs finding themselves swept up in the redundancies.
Financial markets celebrate AI tooling in public valuations, yet internal operational infrastructure struggles to absorb its real-world implications. Banks want lucrative underwriting fees from the AI boom, but risk management committees maintain rigorous defense protocols against unvetted, autonomous execution in day-to-day operations.
Least Privilege Over Vibe Coding: Redrawing the Engineering Perimeter
Goldman’s policy reversal marks the point where the “everyone is a programmer” narrative slammed into regulatory realities. For two years, tech marketing framed autonomous agents as an equalizing force allowing non-technical staff to bypass engineering teams. But in institutional finance, the Principle of Least Privilege remains non-negotiable.
Software engineers are permitted to run autonomous agents because their output is confined by version control and automated verification pipelines. Coding errors are constrained within explicit sandbox boundaries. Traders and bankers, by contrast, operate alongside capital flows and non-disclosure obligations, where rogue local scripts can trigger catastrophic regulatory breaches. The scope of agent permissions ultimately hinges on the blast radius of a potential mistake.
Significantly, the decision to halt agent rollouts originated from Goldman’s internal risk and technology teams, long before regulatory agencies initiated formal reviews. As AI agents evolve from passive autocomplete assistants into active terminal operators, software deployment is no longer just about generation speed. The question of who is allowed to delegate system credentials to a probabilistic model has become the definitive dividing line across financial roles.
References:
- The State of AI report: Goldman Sachs curbs Claude Code access for non-engineering staff.
- Anthropic Form S-1 registration statement: US Securities and Exchange Commission filings.
- Hacker News technical discussions regarding the agent lethal trifecta and prompt injection vectors.
- Barclays technology deployment guidelines and restructuring announcements.