On October 6, 2026, Florida joined forces with Iowa, Montana, and Nebraska to file lawsuits against TP-Link, the world’s leading consumer router manufacturer by market share. This coordinated legal assault comes just six months after the Federal Communications Commission (FCC) enacted a sweeping ban on foreign-manufactured consumer routers.
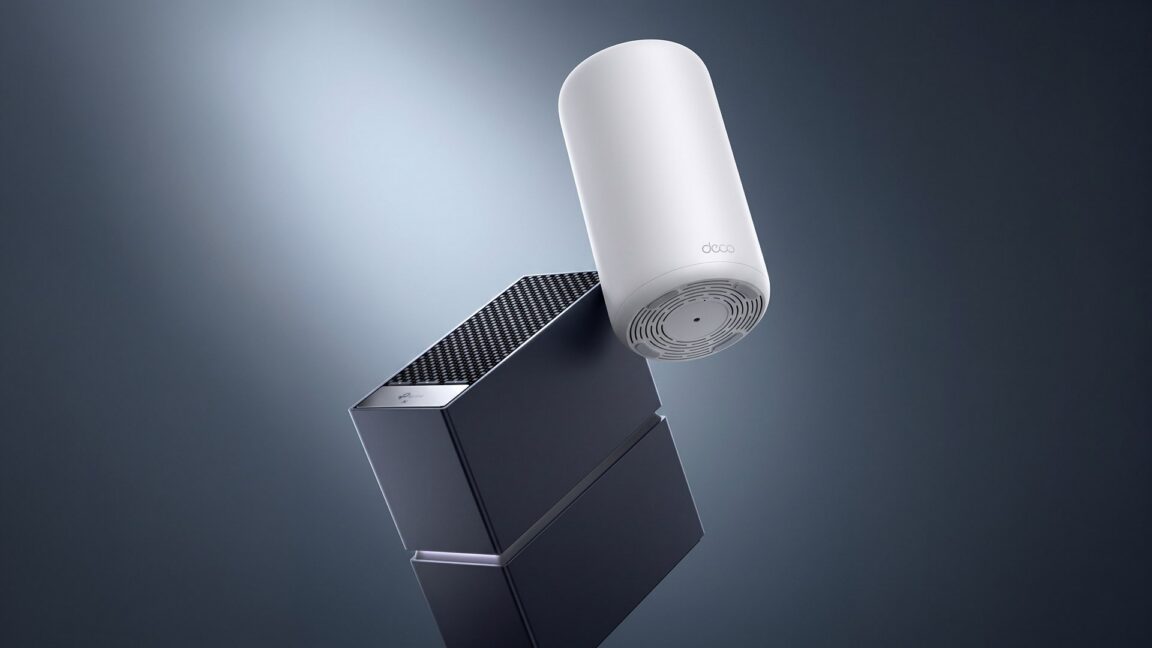 Figure: TP-Link’s Archer 8 Ultra router and Deco 8 Ultra mesh Wi-Fi system. Source: TP-Link (Ars Technica)
Over the past six months, competitors including Netgear, Asus, Amazon’s Eero, and even SpaceX’s Starlink division have secured exemptions from the FCC ban. TP-Link, however, has come away entirely empty-handed. Unable to bring its latest Wi-Fi 8 routers to the US market, the company finds itself stranded, forced to pit legacy hardware against its rivals’ next-generation offerings.
Waivers Choke Off Technical Iteration
The most immediate consequence of the FCC ban is the abrupt disruption of a targeted vendor’s product lifecycle. Hardware access to the US market hinges on FCC Equipment Authorization. Without it, manufacturers cannot sell new devices featuring cutting-edge standards like Wi-Fi 8, and even minor hardware revisions to existing product lines are strictly barred.
For legacy models already on store shelves, the FCC granted only temporary waivers permitting firmware updates—exemptions set to expire on March 1, 2027. Once that deadline passes in a year, the company will face legal jeopardy merely for patching software vulnerabilities on deployed devices. By shutting down approvals for new hardware, regulators have effectively engineered a physical phase-out of targeted brands from the market. Denying an exemption amounts to revoking the ticket to compete in next-generation technology.
The “Made in Vietnam” Shield Collapses
To hedge against escalating regulatory risks, TP-Link adopted a playbook common among international tech firms: it relocated its corporate headquarters to California in October 2024 and submitted filings to state regulators emphasizing that all devices sold in the United States are manufactured in Vietnam.
Florida Attorney General James Uthmeier dismissed this supply chain shift as pure “fiction.” Citing investigative findings published by Bloomberg in April 2025, the complaint noted that locally sourced materials accounted for a meager 0.5% of total input value at TP-Link’s Vietnam facility, with virtually all other parts and assemblies imported directly from China.
When regulatory scrutiny pierces beyond the final assembly site to audit the origin of every component on the Bill of Materials (BOM), the offshore manufacturing workaround falls apart. Core subassemblies and R&D pipelines remain tightly tethered to the original supply chain. Superficial final assembly no longer satisfies the political bar set for hardware provenance.
Consumer Protection Laws as Regulatory Weapons
The legal strategy adopted by the four-state coalition is remarkably calculated. Rather than leaning exclusively on broad, difficult-to-litigate national security claims, prosecutors grounded their complaints in state Consumer Protection Acts.
The lawsuits allege that TP-Link misled consumers by marketing its “HomeShield” security suite as offering “100% protection,” even as its routers were repeatedly compromised by Russia’s GRU and state-sponsored hacking syndicates. In doing so, prosecutors converted standard technical vulnerabilities into legal liabilities under false advertising and deceptive trade practices statutes.
 Figure: Network hardware vulnerabilities are frequently exploited to construct botnets or stage man-in-the-middle attacks. Source: Ars Technica
The states are seeking more than sales injunctions: the complaints demand civil penalties of up to $10,000 per violation, escalating to $15,000 when offenses affect senior citizens, military veterans, or individuals with disabilities. Repurposing consumer protection laws to penalize cybersecurity concerns provides state attorneys general with a low-cost, high-impact weapon that circumvents federal tech trade hurdles.
Home Gateways Become the Geopolitical Frontline
All four state complaints opened with an identical, striking metaphor to define the role of a consumer router: “A router serves as a consumer’s virtual mouth and ears to the Internet. What the consumer says to the Internet comes out of the router’s mouth, and what the Internet says back goes through the router’s ears. If compromised, it can whisper lies in both directions, impersonating the consumer and creating a foothold in the consumer’s own home for state-sponsored cyberattacks.”
This personified depiction exposes how law enforcement and the judiciary fundamentally view home networking gear. Small Office/Home Office (SOHO) routers run continuously 24/7, rarely receive firmware updates, and sit exposed directly on the public internet. This makes them ideal launchpads for Advanced Persistent Threat (APT) groups building stealthy proxy networks. Far from being harmless plastic boxes that cost a few dozen dollars, home gateways are now treated as critical frontline infrastructure in geopolitical cybersecurity conflicts.
TP-Link responded by asserting that it complies fully with US privacy regulations, conducts comprehensive security testing, and commissions trusted third-party laboratories to validate its hardware. The company emphasized that it does not and will not share customer network data with foreign governments. Yet under a regulatory regime operating on a presumption of guilt, unilateral technical assurances carry little weight. When market entry criteria shift from objective engineering standards to supply-chain pedigree audits, tech exporters face a regulatory gauntlet with little room to maneuver.
Reference Links:
- Ars Technica Report
- FCC Router Ban Policy Announcement